Governance, Risk & Compliance for financial institutions
Manage risks and controls without spreadsheets. One GRC platform for banks, insurers and pension funds, built for European regulation such as DORA.
Risk and control data often lives in spreadsheets and disconnected systems. That leads to:
 Fragmented registers that hide trends and duplication.
 Scores that stay the same when the impact changes.
 Risk appetite breaches that surface too late.
All risk and control data in one place, scored and continuously in view:
 Preloaded taxonomies for consistent classification.
 Quantitative and qualitative risk scoring.
 Instant alerts on breaches, audit-ready by design.


One platform for every perspective
Risk and compliance is no longer a box-ticking exercise. It is a strategic function, and it demands an equally strategic platform. CERRIX gives every stakeholder in your organisation a personalised view, tailored to their role and responsibilities. One platform, every perspective, built for financial institutions that need more than a spreadsheet.
A smarter way to govern risk and controls
CERRIX brings risks, controls, risk appetite and trends together in one workspace. Your teams get the overview and context to make well-informed decisions, and everything is ready for audit.
Multi-level risk taxonomies
Pre‑configured structures clarify classification across entities, ensuring every risk is captured, categorized, and managed consistently. This reduces ambiguity and strengthens oversight across complex operations.
Dynamic risk scoring
Adjust quantitative or qualitative models in seconds when exposure changes, so every score stays current.
Risk time-travel analysis
See how risks develop over time, so you spot trends and adjust course earlier.
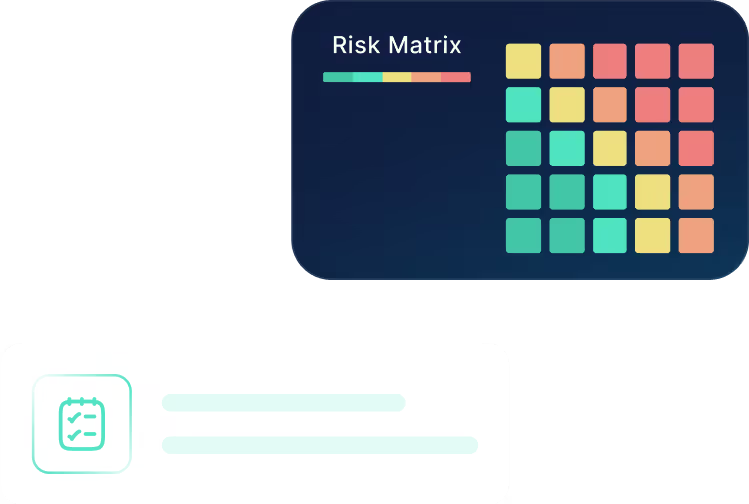
Align with risk appetite
See at a glance whether risks stay within your strategic goals and thresholds.
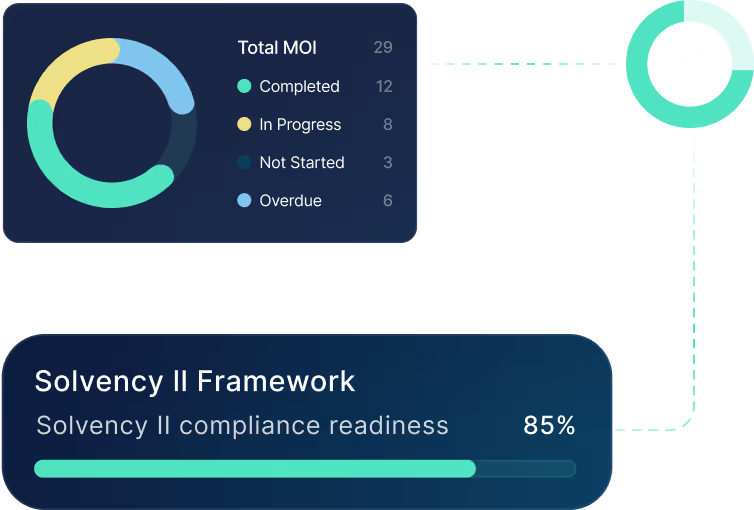
Integrated risk management
Link risks to controls, processes, projects and regulatory frameworks.
Solving real-world GRC challenges with one smart platform

Aligned stakeholders across risk, compliance, and audit

Reliable data that supports better decisions

Tailored configuration that matches your governance frameworks

Phased onboarding that reduces risk and accelerates adoption
GRC implementation that goes beyond tool setup
Rolling out GRC implementation is more than launching software. It’s about creating clarity in your processes, consistency in your data, and aligning and motivating all 3 lines to work together. At CERRIX, we guide you through every step.
Understand, align, prepare
We begin by forming a strong foundation:
Configure, Customize, Validate
We tailor the platform to your organization’s needs:
Test, Train, Launch
We ensure your team is ready to succeed:
Evaluate, Improve, Expand
Post-go-live, we help you evolve:
See how clients use CERRIX

How Blauwtrust Groep centralized its control framework in CERRIX GRC Platform

How VGZ Strengthens Risk & Compliance Operations with CERRIX


Transforming Compliance: How Menzis Gained Efficiency and Real-Time Insights with CERRIX


Structuring Risk and Audit Across Teams: Haier Europe’s Journey


Transforming Risk Culture: How Stater Strengthened First-Line Ownership and Assurance with CERRIX
Enterprise-grade security

Data protection
ISO/IEC 27001 certified, in line with the international standard for information security.

Control assurance
ISAE 3402 Type II: our internal controls are independently audited.

Financial sector readiness
FSQS-NL registered and pre-qualified for procurement by banks and insurers in the Netherlands.


